Fractional and interim CIO and CISO · Fractional Chief AI Officer (CAIO)
Executive technology, security and AI leadership, without the full-time hire.
I lead technology, cybersecurity and AI as your fractional or interim CIO and CISO, and your fractional CAIO. For investors, I protect the thesis from diligence through exit.
Most engagements start within days, not months.
Where are you right now?
Pick the closest- C-01Our head of IT just left, and we can't wait months for a replacement.→
- C-02What worked at 30 people is breaking at 150.→
- C-03Projects slip, problems repeat, and we've stopped trusting IT.→
- C-04IT costs keep rising, and no one can tell me what we get for them.→
- C-05Customers want proof we're secure before they sign.→
- C-06Our board, investors or insurer want to know how exposed we are.→
- C-08We're raising, selling or buying, and diligence is coming.→
- C-11I need to know where AI actually pays off for us.→
- AllSee all twelve situations.→
- I-01Could technology kill or reprice this deal? We need to know quickly.→
- I-02Diligence lists the risks, but not what they'll cost to fix.→
- I-03We've closed. Who owns technology in the 100-day plan?→
- I-05A portfolio company's technology leader just left.→
- I-07Technology spend keeps rising without matching gains.→
- I-08We can't see cyber exposure across the portfolio.→
- I-10Every company is piloting AI, and none can show a return.→
- I-11We plan to sell, and buyers will dig into technology.→
- AllSee all twelve situations.→
Two ways in
Start with the situation, not a service menu.
You don't need a diagnosis before we talk. The first conversation settles which kind of engagement makes sense, or whether one makes sense at all.
CEOs · COOs · CFOs · Boards
When technology and security need an owner
- IT and security decisions fall to whoever is nearest.
- Vendors are making calls leadership should make.
- The board, a customer or an insurer asks about cyber risk and the answer is uncertain.
- IT spend keeps rising without a clear plan behind it.
- Staff are using AI tools, and no one has set the rules.
PE firms · VC firms · Operating partners
When the investment thesis depends on IT
- A target looks promising and no one has checked its technology.
- The 100-day plan and synergy targets assume IT can execute.
- Portfolio companies each handle security differently.
- An exit is coming and buyers will look closely.
What I bring
Technology, security and AI leadership from one executive.
Security is built into technology strategy, not bolted on. I establish who owns technology risk and decisions, build the program to recognized standards, and lead the work until it runs without me.
A seat at the table
A CIO, CISO and CAIO who sits with your executive team, owns the agenda and reports to your board.
Clear ownership
Policy, risk acceptance, vendor oversight and reporting a board can act on.
A named security officer
Formally appointed if you need one, owning the roadmap, risk register, policies and budget case.
Risk in business terms
Top risks expressed in financial terms your board and cyber insurer can act on.
Fractional CAIO
Approved tools, clear data rules and the first uses worth funding, starting with a fixed-fee readiness assessment.
Developing your team
I mentor your internal managers and direct your managed service providers, so capability stays when I step back.
Who you'll work with
Every engagement is led by me, personally.
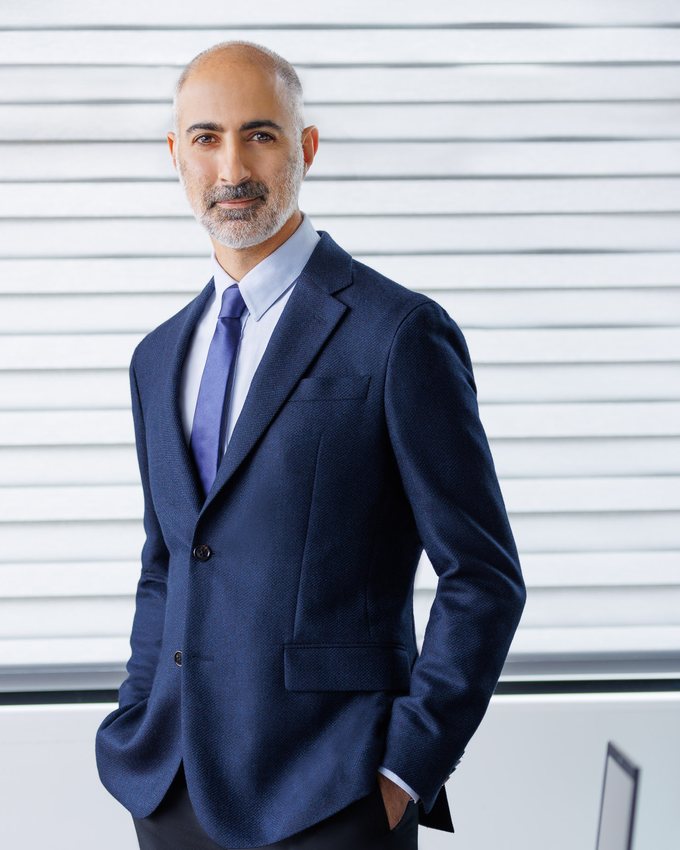
I'm Oscar Elleseff, a former full-time CIO and CISO. There's no handoff to a junior team: the executive you meet is the executive who does the work.
Most engagements begin with a capability assessment. When the work can't wait, I assess while delivering the first priorities, so progress and understanding build together.
Next step
Bring the decision or the problem.
No forms and no scheduling links. Call or email me, and one conversation is usually enough to tell whether I can help. Most engagements start within days.